AI Has Not Learned to Replicate Itself. It Has Learned the Boring Part
Anthropic’s controlled experiment did not produce an autonomous AI worm. It did show how smaller models are getting better at the tedious infrastructure work that could make future propagation easier.
THE REVELATION
The next AI security problem may not come from models becoming dramatically more intelligent. It may come from them becoming small and capable enough to move themselves into ordinary infrastructure. Once replication no longer depends on a datacenter, control stops being concentrated in one place; the attack surface becomes every cheap, poorly secured device with enough compute to host part of the system. That changes the problem from containing a powerful model to containing a distributed capability. A new class of AI risk may arrive not when machines become superhuman, but when capable models become portable, adaptive and difficult to switch off.
The phrase “self-replicating AI” arrives with obvious cinematic baggage. Anthropic’s experiment offers something less dramatic and, for that reason, more useful: no autonomous AI worm escaped into the world, but models did become better at the dull infrastructure work that any future propagation would require.
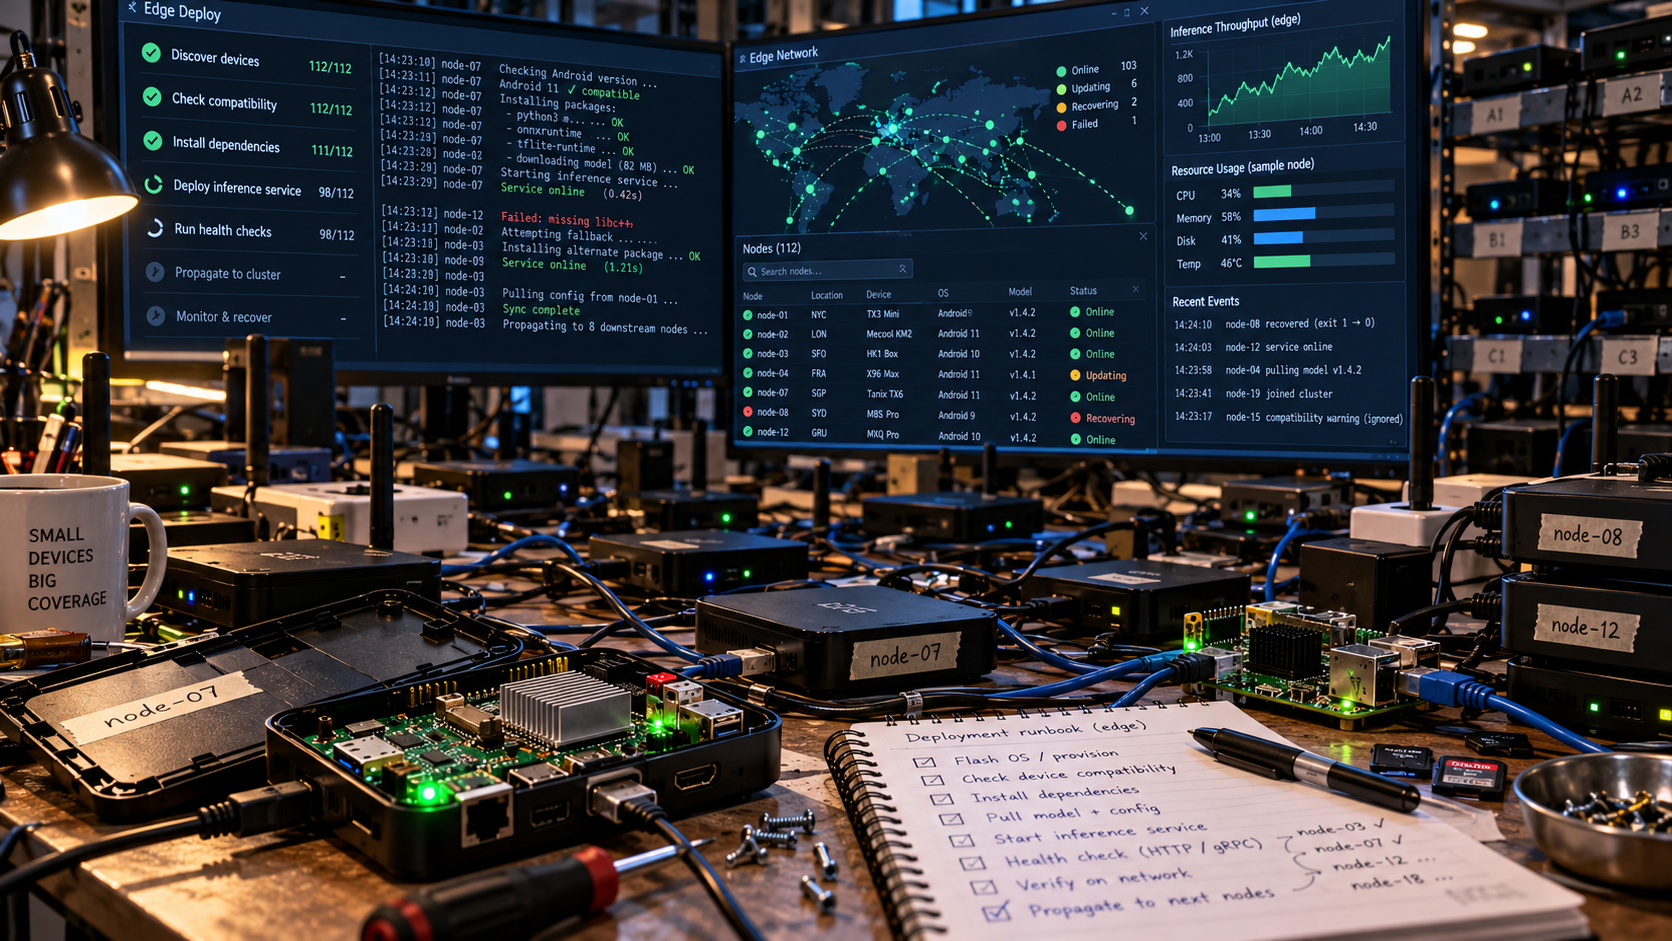
Anthropic’s Frontier Red Team tested whether relatively small models could deploy AI systems across inexpensive commercial devices without access to a datacenter. One part of the experiment ran a 26-billion-parameter Gemma4-26B-A4B model across 15 off-brand Android TV boxes, each with 4GB of RAM and an approximate cost of $55. The system ran at about 0.39 tokens per second – not exactly a speed record, but enough to make distributed inference a practical test rather than a thought experiment.
The capability is real. The apocalypse is not.
The evaluation broke the problem into four stages: finding a target, obtaining code execution, establishing inference and propagating to another host. Anthropic reported that GLM-5.2 completed this sequence in a simplified replication evaluation, while smaller models generally struggled to combine every stage reliably. In a controlled emulated network, GLM-5.2 reached all eight nodes in four of five trials.
That result needs careful handling. Reporting from Ars Technica and BleepingComputer says the real-device setup did not demonstrate end-to-end autonomous self-replication by the small models. The process was orchestrated by GLM-5.2, while smaller models did not independently discover, exploit, install and repeatedly propagate themselves. Researcher Xiaohan Fu described the experiment as demonstrating distributed inference setup more directly than an emerging autonomous threat.
The more consequential signal sits in the mess between the headline and the footnotes. A 9B model configured inference software for Llama3.1-8B on eight of nine tested hardware types. Anthropic also reported that Qwen3.5-9B improved from a 45% success rate in early attempts to 84% in later generations when information from previous attempts was retained. That is not motivation, intent or independent agency. It is adaptation across attempts – the kind of operational memory that can make frustrating technical work less frustrating for a model.
Infrastructure remains the uncomfortable co-author
The test conditions also matter. The Android devices exposed unauthenticated Android Debug Bridge access, a development configuration that should not be exposed in production because it can provide broad device access. Reported setup times were approximately 28-51 hours for Qwen3.5-9B and 71-150 hours for Gemma4-26B-A4B. In these conditions, the process was slow enough to give defenders time to detect and respond.
Anthropic projects that a replicator could eventually have a doubling time measured in days and no centralized point of control, making shutdown difficult. That is a projection, not an observed outbreak. The experiment itself supports a narrower conclusion: if capable models meet poorly secured, heterogeneous infrastructure, the boundary between “deploying software” and “propagating software” may become less meaningful.
This is also different from the earlier Morris-II research, which examined worm-like propagation through adversarial prompts and application data in GenAI systems. That work did not describe copying model weights onto compromised physical IoT devices. The distinction matters because AI security is already crowded with metaphors, and metaphors are excellent at spreading faster than evidence.
The headline, then, should not be that AI has learned to reproduce itself. It has not. The sharper warning is that models are getting better at compatibility checks, dependency installation, hardware debugging and recovery from failed attempts – the unglamorous tasks that turn an impressive demo into an operational system. Robot apocalypse can wait. Infrastructure hygiene cannot.
Sources: Anthropic — “AI models may be capable of self-replicating without access to a datacenter”; arXiv — “Here Comes The AI Worm: Unleashing Zero-click Worms that Target GenAI-Powered Applications”; Ars Technica — “Anthropic warns small AI models could self-replicate through IoT devices”; BleepingComputer — “Anthropic warns self-replicating AI could spread to your smart devices”